Category: MikroTik

  • Can’t fish Ethernet? Use “invisible” fiber instead.

    My family owns a NYC townhouse, and with that I had Cat6 cables put in on each floor.

    However, more recently, one of the Cat6 cables has gone “bad,” meaning it only does 100 Mbps. While we are nowhere close to Gigabit speeds, very less multi-Gig (despite me having had symmetric Gigabit in the past), it’s still not something I’m happy about.
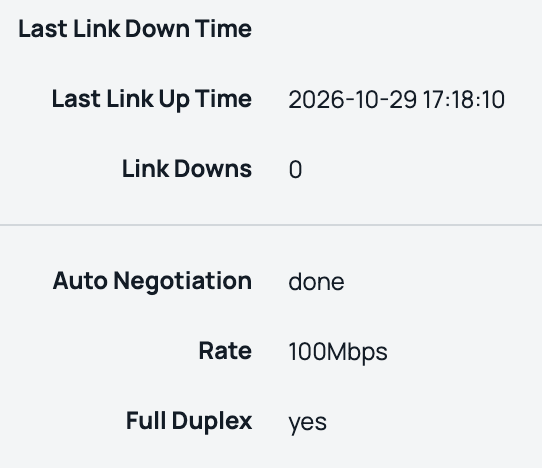
    What do you mean only 100 Mbps? My switch and AP support 2.5 Gbps.

    The most common approaches in my scenario are:

    • Fish a new cable
    • Abandon the cable and use wireless mesh

    However, there are a few issues:

    • The cables were fished in a funky way, and considering how clumsy I am I don’t want to cause more damage
    • Our walls are thick, meaning wireless mesh would suck

    When I did use mesh on HPE AP25s (the APs I use), the performance was 120 Mbps at two prior homes, that with thin walls and fiber. I also want VLAN segmentation so a typical consumer Eero or Orbi won’t work.

    So what did I do? “Invisible” fiber between two floors.

    In case you didn’t know, there are special types of fiber cables originally designed for apartment retrofits. This is to avoid landlord/HOA complaints. Our prior place had Verizon Fios via these cables in the hallway.

    But these cables are also sold on Amazon and AliExpress for people who’re in rentals or don’t want to fish cables.

    So how did I do it?
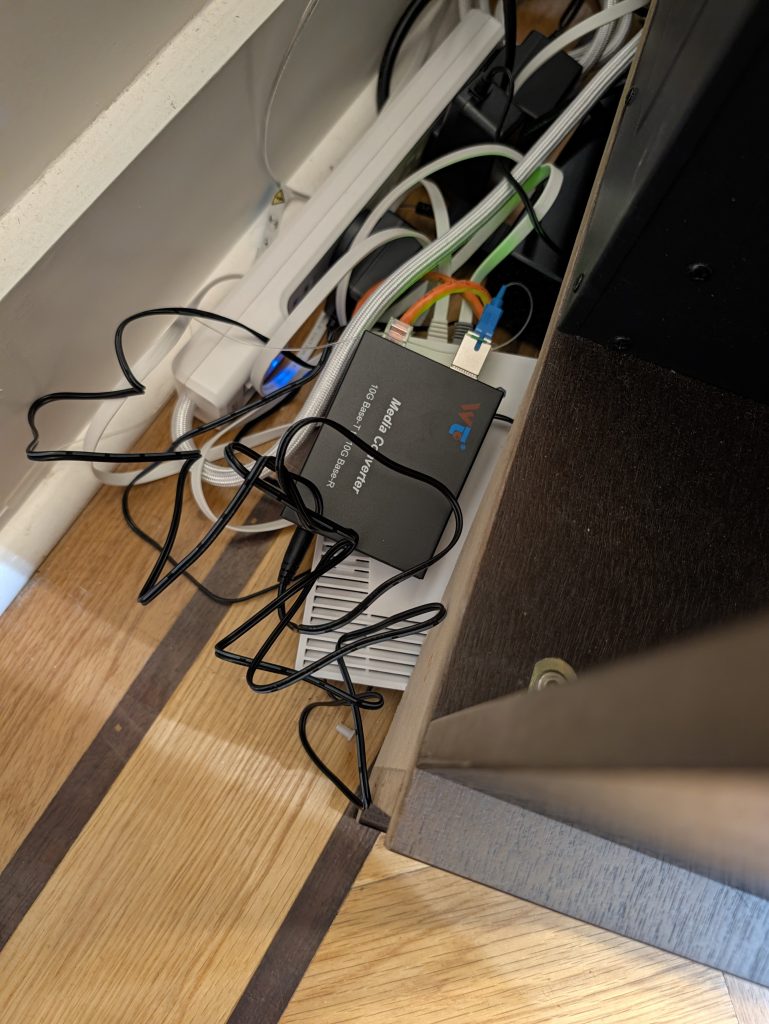
    Galore, the endpoints of my 20m/60ft ‘fiber in the home’ loop.

    Switch

    While there are SFP+ switches, I already had an unused MikroTik CRS304-4XG-IN, so I just used it here. It’s technically copper 10G, but I’d lose more by trading it for a SFP+ switch so I’ll just keep it. Not to mention copper SFP+s get hot.

    Media Converters and Transceivers

    I used two media converters and a pair of bidirectional SC SFP+s.

    The SFP+s use the same SC connector used in PON networks, but otherwise use Active Ethernet. I’m not sure if they’re using IEEE standards or are proprietary on the glass, but I’ll assume the latter.

    While there’s copper on the media converters, the other option would be to replace our switch which I’ve mentioned is not the best idea.

    The Fiber

    While the fiber can (and is designed to) be superglued, I chose to use the included adhesive instead. Why? In case I ever have to remove it, which has happened before.

    That’s the same reason why I did the basement AP25 using command strips when everyone else just drills the mount.

    While our fiber is UPC, our transceivers support both SC fiber types.

    Conclusion

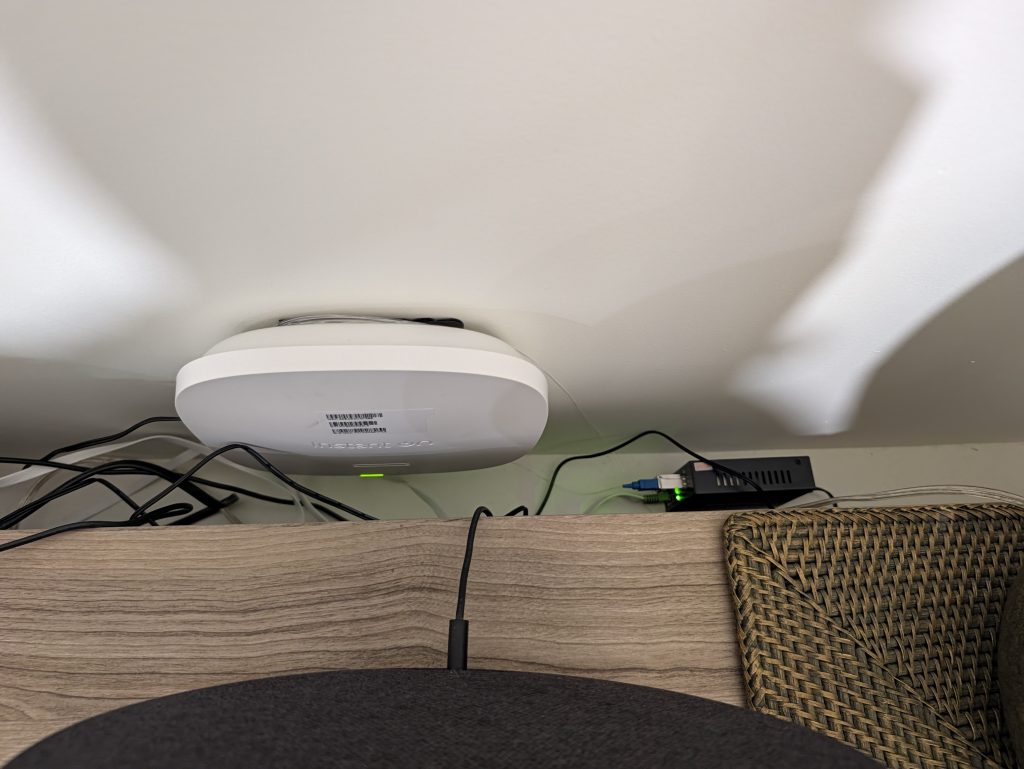
    If I look at the Instant On portal, I’m posting this from my MacBook connected to the new ‘fiber in the home’ loop (via an HPE AP25).

    While we currently lack fiber-to-the-home (Mamdani, please fix Fios rights of way!), I’m still happy I could DIY a fix for a Cat6 cable with bad pairs.

    In fact, while I don’t have multi-Gig I could still get a respectable ~300 Mbps:
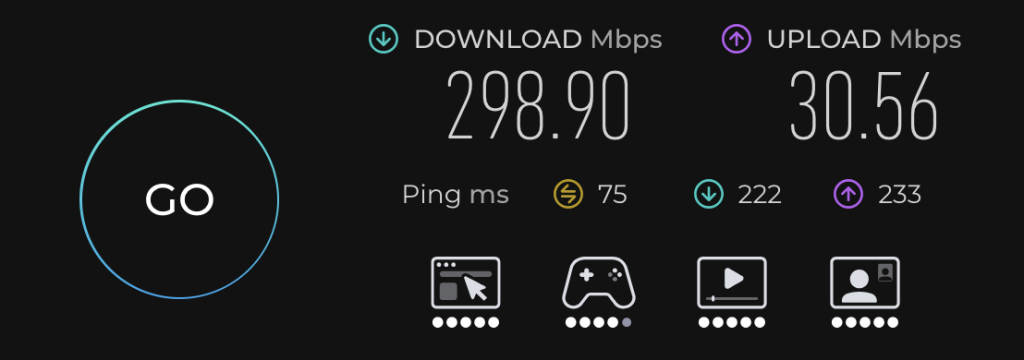
    So yes, even if you don’t have fiber to the home, fiber is still useful in a home network. As it saved me from having to hire a contractor and possibly tear our walls. Not to mention a $1500 Samsung TV is on the wall the “defective” Cat6 cable is behind.

  • MikroTik CRS312-4C+8XG-RM: Combo SFP+/RJ-45 ports not detecting SFP+ on modern RouterOS versions

    I re-purchased a MikroTik CRS312-4C+8XG-RM off eBay after selling mine (which I had for 4.5 years) this January. This is to provide network to four HPE Instant On AP25s across our townhouse via 2.5G copper (which are DC powered now), as well as my Intel 285K desktop and lab bench via 10G copper

    One problem with the CRS312-4C+8XG-RM on newer RouterOS versions is that the combo port doesn’t autodetect out of the box. You are basically stuck manually setting it yourself, or using RJ-45. Or are you?

    However, this is easy to change. To fix it:

    /interface ethernet
    set [ find default-name=comboX ] combo-mode=sfp

    Replace X with the combo port you want as a SFP+. This can be done for one or more ports.

    This way, I can connect it to a CRS317-1G-16S+RM (my core switch) in VLAN trunk mode.

  • Doing VLAN trunk and access ports on MikroTik CRS/RouterOS

    Most of the switches in my homelab are MikroTik CRS switches, although I am getting a UniFi PoE switch (MikroTik didn’t make a 2.5G PoE switch, that’s why).

    I use two CRS304-4XG-IN switches to connect desktop computers to the 10G LAN, but wanted my desktops on a separate VLAN.

    On my network, I use VLAN 4 for desktops.

    The configuration you need is:

    /interface bridge
    add admin-mac=XX:XX:XX:XX:XX:XX auto-mac=no name=bridge vlan-filtering=yes
    /interface bridge port
    add bridge=bridge comment=defconf interface=ether1
    add bridge=bridge comment=defconf interface=ether2 pvid=4
    add bridge=bridge comment=defconf interface=ether3 pvid=4
    add bridge=bridge comment=defconf interface=ether4 pvid=4
    add bridge=bridge comment=defconf interface=ether5
    /interface bridge vlan
    add bridge=bridge tagged=ether1 untagged=ether2,ether3,ether4 vlan-ids=4

    The bold parts are important, and I will explain what they are:

    • vlan-filtering=yes in the /interface bridge means you will filter for VLANs. This is required for VLAN trunk/access ports.
    • pvid=4 in the /interface bridge port means the specific port will use VLAN 4.
    • tagged=ether1 in the /interface bridge vlan means the trunk/tagged port is ether1.
    • untagged=ether2,ether3,ether4 means the ether2-4 ports are access ports
    • vlan-ids=4 means we are establishing a bridge on VLAN 4.

    Hopefully, this helps you set up VLAN trunking on a MikroTik CRS/RouterOS switch.

  • MikroTik: Add DNS Forwarding Entry for Active Directory DNS

    Also, why didn’t anyone tell me about match-subdomain=yes?

    For almost two years, my homelab’s core router has been a MikroTik, namely a CCR2004-16G-2S+ and then a CCR2004-16G-2S+PC. I also run a FreeBSD Samba Active Directory domain controller.

    The common ‘solution’ is to use domain wildcard regex and that’s usually not pretty.

    Then I learned about the match-subdomain=yes and it worked wonders, that combined with ttl=0s.

    Keep in mind that by using this guide, I am assuming you’re using the DNS server on a MikroTik router, versus an external resolver.

    If you’re using MikroTik’s resolver, add the following configuration:

    /ip dns static
    add forward-to=IP match-subdomain=yes name=DOMAIN ttl=0s type=FWD

    Replace IP with your DC’s IP address, and DOMAIN with the domain name used by AD.

    Note: you need ttl=0s, otherwise it gets out of sync. match-subdomain=yes is a shortcut Google never told us about (even without “AI” responses), but is ultra useful here.

    If you wish to forward reverse DNS entries, you can do:

    /ip dns static
    add forward-to=IP match-subdomain=yes name=xx.in-addr.arpa ttl=0s type=FWD
    add forward-to=IP match-subdomain=yes name=yy.ip6.arpa ttl=0s type=FWD

    Replace IP with the IP address of the DNS server, and xx (IPv4) and yy (IPv6) with the Reverse DNS zones used by your network.

    This should give you AD DNS using MikroTik’s DNS server.